Ambition matrix example
- Part of a management system, see Quality management software -
From Metaware's knowledge center.
Keywords: quality management, quality manager, ISO, ISO 9000:2026, ISO 9001, ISO 27001, NEN 7510, risks, risk management, risk management, risk matrix, threats, opportunities, cUnroll Framework
Ambition matrix: why?
Many organizations now have a risk matrix, but how many organizations also have an ambition matrix? With the arrival of the new ISO 9001:2026, that question seems more relevant than ever. In the draft version, opportunity management gets its own paragraph: 6.1.3 Opportunities. In this way, the standard makes it clear that opportunities are no longer the positive brother of risks, but an independent part of good quality management. The question will soon be not only which risks you have identified, but especially which opportunities you have consciously chosen to take. What opportunities have been identified? What actions have been taken in response to this? And perhaps the most important question: what did it ultimately yield? This evaluation belongs in the management review and makes it visible whether ambitions have actually been achieved.
That requires a different way of thinking. Not only control, but also improve. Not only prevent, but also develop.
Ambition matrix: what can you do with it?
An ambition matrix is a simple but effective tool to map, develop, evaluate and prioritize opportunities. As indicated, it is a mandatory process in most management system standards (ISO 9001, ISO 27001, ISO 14001, etc.) and increasingly explicit in the latest standards. An ambition matrix is often presented in tabular form, with, for example, Feasibility on one axis and Value on the other. The different cells in the table show the combination of the two criteria, often shown in color.
Measures must be taken to make better use of an opportunity. This can increase the feasibility and/or value. Just the opposite of a risk matrix. The (control) measures are in turn part of the control framework.
Example. You have a real chance of having less product failure with a new analysis method. A good plan of action increases the feasibility and by a sophisticated application of this analysis method, the dropout can be further reduced (and thus the value further increased).
Ambition matrix applied
The ambition matrix can be applied analogously to a commonly used risk management method. By incorporating these into software tooling, it is much easier to implement it (together!) within your own organization.
Inventory of all processes and assets within your own organization: where are the opportunities for improvement. What are the ambitions? A SWOT analysis is a commonly used 1st step for opportunities (and threats/risks).
Opportunities are mapped out for each process. It is useful to analyse and assess this together with different disciplines, from different angles.
The outcome of this step is a classification of the probabilities. Both feasibility and value are estimated on a scale of 1 to 5.
The result of this step is an overview of probabilities on a scale from I to IV, indicated in colors according to the table below. This clearly shows which opportunities are 'quick wins', 'worthwhile', 'limited profit' or 'low priority'.
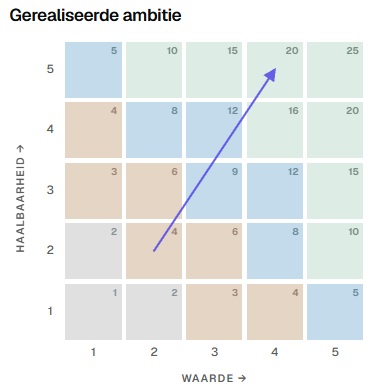
The identified opportunities are compared with the established acceptance criteria. Is it useful to further develop the opportunity or is it possible to further increase the success (feasibility/value) with a management measure?
The measures for the opportunities with a possible success are laid down in the control framework. This immediately guarantees follow-up.